The developer's toolkit for web testing & security.
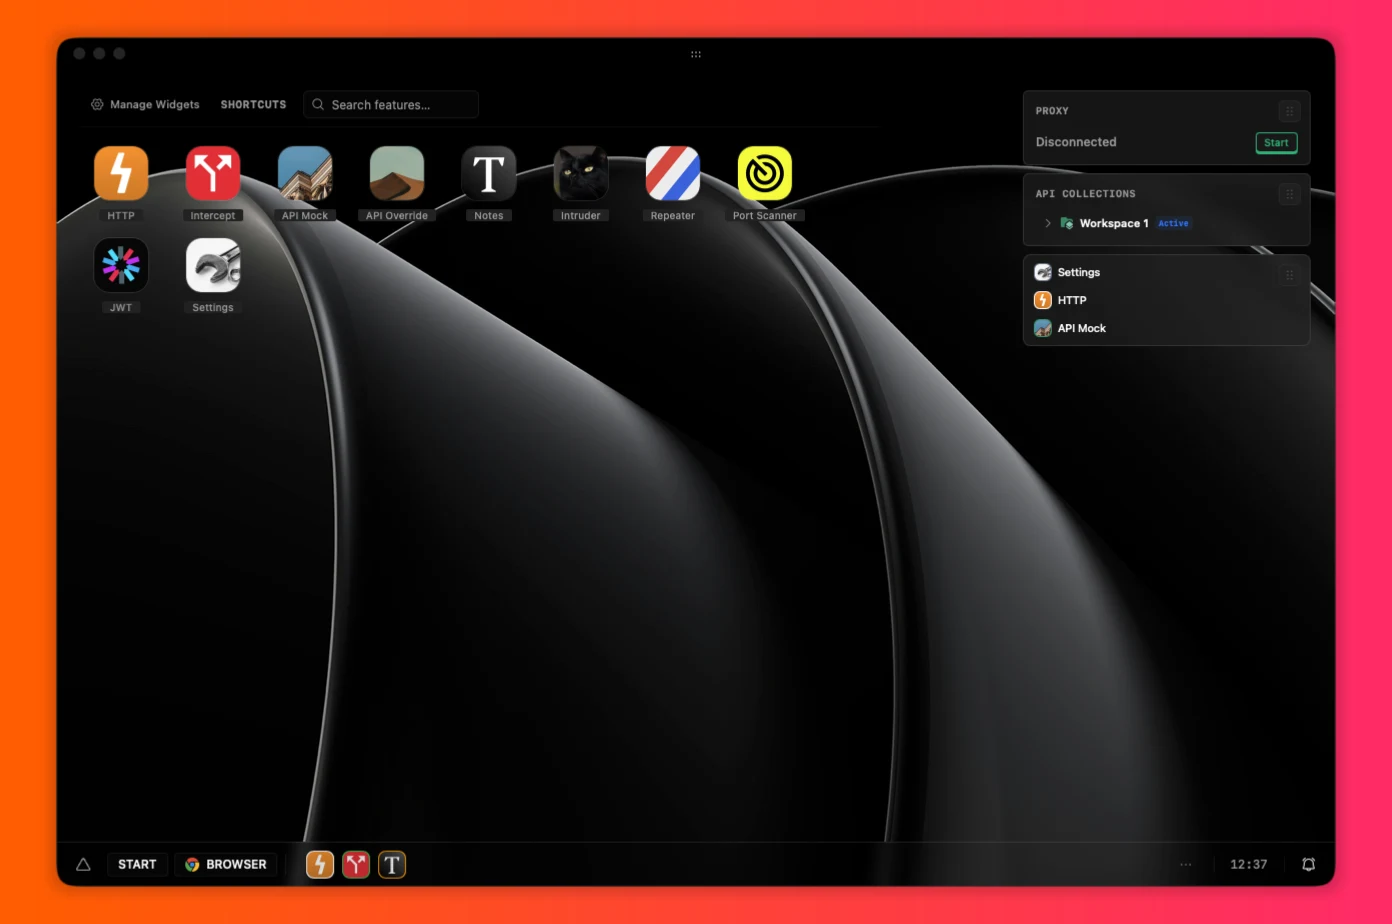
Desktop workspace for HTTP inspection, API testing, and security research. Intercept requests, replay traffic, and debug endpoints in real time.
macOS available now · Windows build in progress
- Runs entirely on your machine
- No account required
- No cloud dependency
Built-in modules for every phase of testing.
Dedicated desktop tools engineered for web application reconnaissance, traffic analysis, and vulnerability discovery.
HTTP History
Core ProxyLive Traffic Stream & Deep Inspection
Capture and inspect every HTTP and HTTPS transaction in real-time. Analyze request headers, query parameters, multipart bodies, and response latency with zero lag.
Who is Hexbuffer for?
Tailored for security engineers, penetration testers, and developers requiring fast, private local reconnaissance.
Penetration Testers
A dedicated local workstation for intercepting, inspecting, and manipulating live target HTTP traffic.
Security Researchers
Deep request and response payload inspection with automated fuzzing and token tampering.
Developers & QA
Debug web APIs, mock scenarios, and verify endpoint behavior with instant request replay.
Try Hexbuffer on your next target.
Install from the terminal, point the proxy at your target, and start inspecting traffic in minutes.